Pre-launch audit · free · MIT
Ship AI-written code without shipping AI-written bugs.
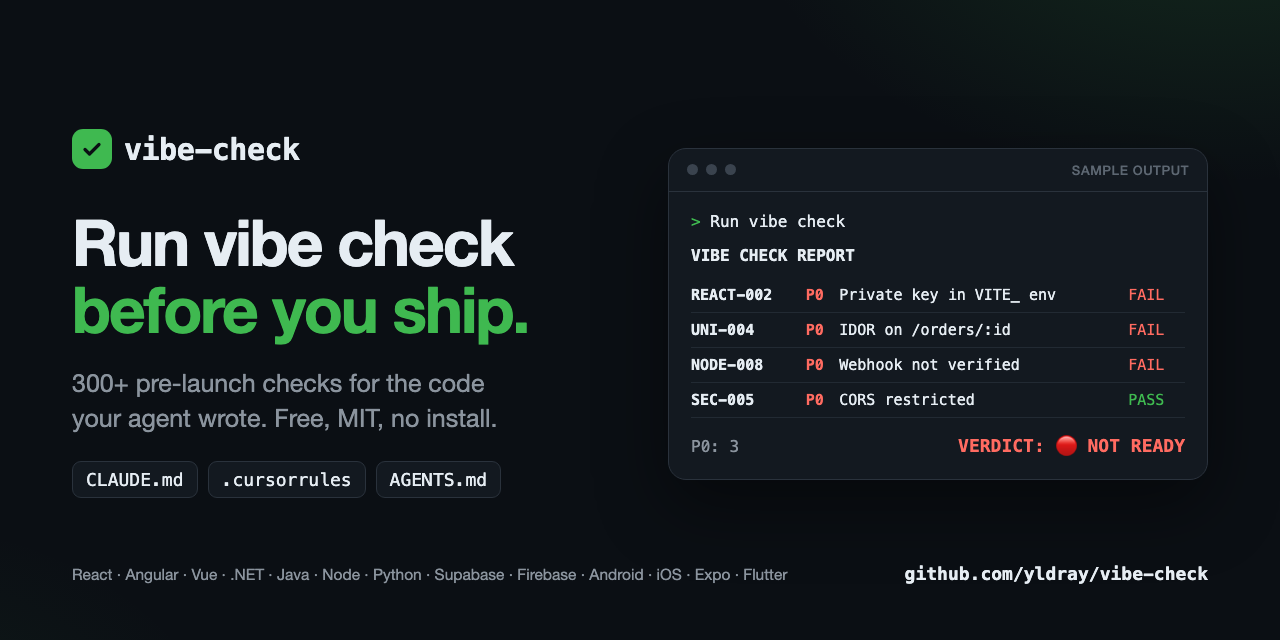
One file tells Claude Code, Cursor or Codex how to audit your app before launch: secrets, auth, payments, store rules and each stack's chronic bugs. Your AI audits the code it wrote and nothing changes until you approve.
Set it up once
Claude Code, in the chat:
/plugin marketplace add yldray/vibe-check
/plugin install vibe-check@vibe-check
Cursor, Codex and others, in your project root:
npx @yldray/vibe-check installThen tell your agent "Run vibe check", or "quick vibe check" for P0s only.
Bugs it's built to catch
These shipped in real apps built with coding agents. Each one is now a check.
| What happened | Check |
|---|---|
| The login code came back in the API response "for testing". Anyone who knew an e-mail could sign in as that user. | AUTH-009 |
| The login rate limit keyed on the reverse proxy's IP, so the whole platform shared one quota. Twenty requests locked everyone out. | DOTNET-032 |
| Two taps on "Generate" sent two requests. The duplicate check ran outside the lock, so the user paid twice. | PAY-006 |
The deploy went green, but the artifact had dropped the .next folder. The site answered nothing. | REACT-030 |
| A column-rename migration moved the column but not the stored values. Existing profiles became unreadable. | OPS-001 |
The store build silently fell back to localhost for its API. Nothing worked for real users. | UNI-018 |
What you get
Every stack
React, Angular, Vue, .NET, Java, Node, Python, Supabase, Firebase, Android, iOS, Expo, Flutter.
Store and legal rules
App Store, Google Play, privacy, account deletion, payments with PayTR, iyzico and Stripe.
A clear verdict
Every check gets an ID, a status and file:line. Any open P0 means NOT READY.
Read-only and plain text
Markdown you can read in two minutes. It never prints a secret value.
Benchmark
Two intentionally vulnerable projects with 22 planted bugs, one prompt: "quick vibe check". Claude Code found 22/22, Cursor 22/22, Codex 20/22 plus 2 partial. Run it yourself.
Block a merge in CI, no LLM needed
- uses: actions/checkout@v5
- uses: yldray/vibe-check@v1
Secrets, .env in git, keys shipped to the client, open CORS and GitHub Actions injection. Locally: npx @yldray/vibe-check scan.
Passed? Show it.
On a 🟢 READY verdict the agent offers a README badge: